-
A Short Thread on peoples’ understanding of “End-to-End Encryption”
Unrolled Hi Colm! I can't remember seeing—at any time in my experience of end-to-end encryption since 1991—anyone using the term do describe the "hop-at-a-time" process that you describe below. So, in a short thread? I'll attach a few resources to help everyone. Firstly, heres my video on the Duck Test for End-to-End Secure Messaging Secondly,…
-
High Performers of Low Trust #tiktok #funny #wellilaughed
Try to avoid working with people you can identify via this one weird trick:
-

ICYMI: @LordJimKnight (who has abandoned Twitter) proposes in the #OnlineSafetyBill that platforms must know the nationality and/or physical location of their users, lest VPNs (etc) are used to circumvent OSB restrictions
This proposal is misconceived, illiberal and practically totalitarian; the Internet is not designed with the concept that data (i.e. speech) has a nationality, and therefore the obligation would be on platforms to obtain and maintain nationality or physical location of their users (rather than utilise communications metadata) in order to hamper people who might use…
-
A short thread on implementing properly private end-to-end encrypted messaging on your global megaplatform
Alec’s Response Quite; when building FB Messenger “Secret Conversations” in 2015/16, our analogous thinking was: 0/5) app-only 1) privacy precludes visibility 2) compensate with better report flows 3) fix cards mañana with local rendering 4) photo re-encoding is a thing 5) webclient will be hard re: Web-Client, there were more significant architectural issues with in-browser…
-

Resource for Journalists: How best to frame your article criticising @ElonMusk for adding #Encryption to @Twitter DMs. Questions to ask, resources to consult.
Note: this is a “living” document. Check back for updates.Last updated: 5 May 2023 around 0800h London time. Hi! Thank you for reading this! If you’re a journalist and you’re going to write something about Twitter adopting Encryption for Twitter Direct Messages, it’s really easy to adopt the frame that: “Elon is doing it, so…
-
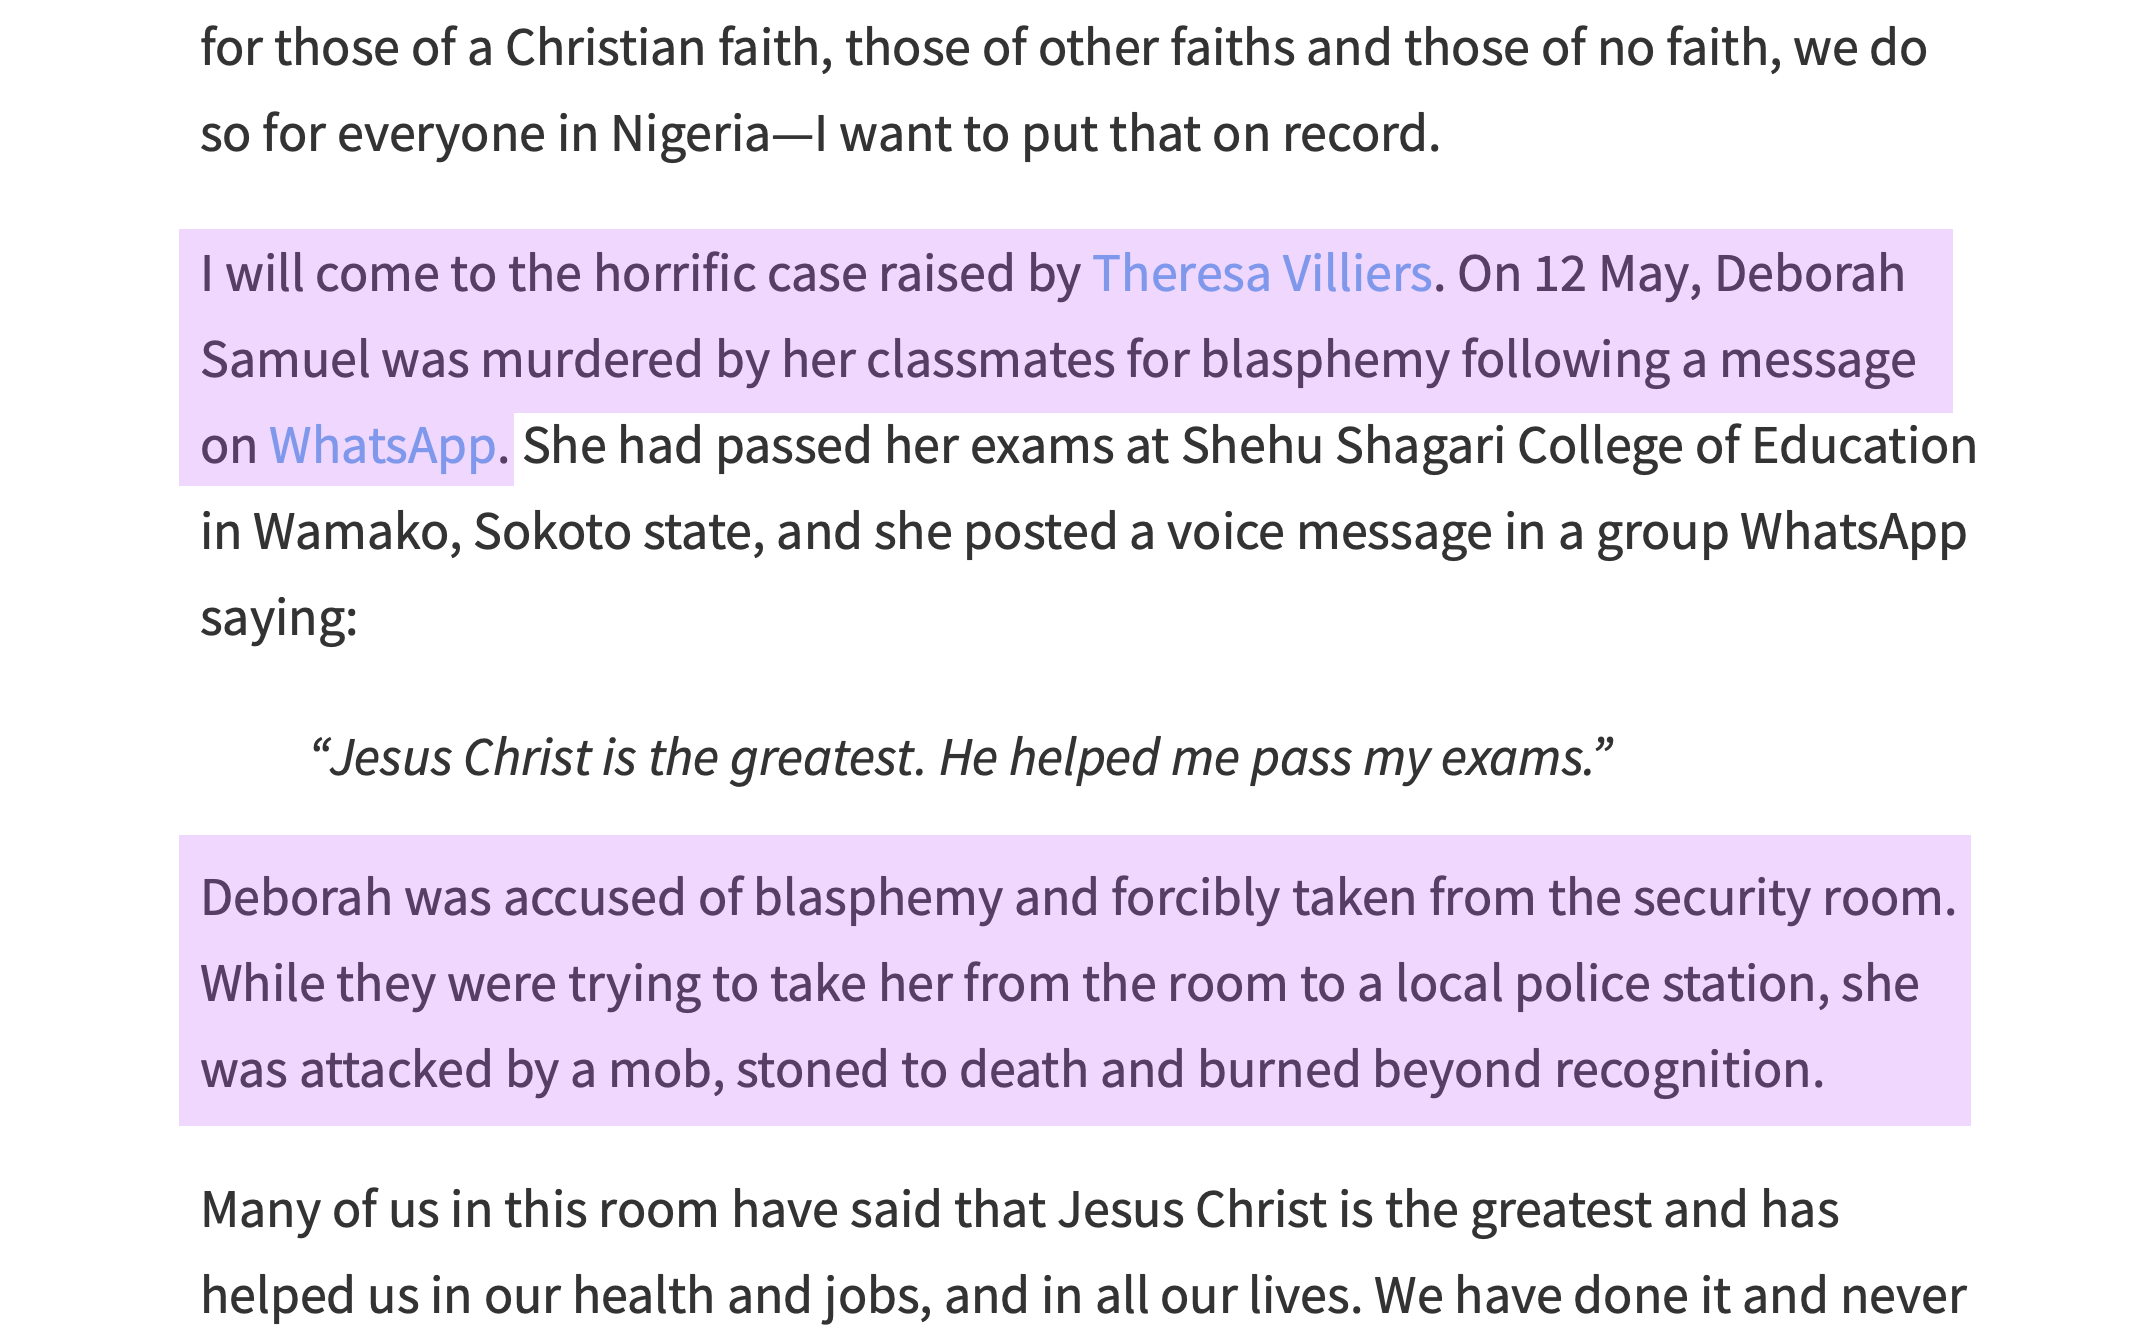
Re: #OnlineSecurityBill & #ChatControl demands to filter WhatsApp messages for content legality, one must wonder if the UK & EU Governments would be content to extend such features to northern Nigerian or Uganda? #ChatKontrolle #LGBT
I have a family link to northern Nigeria[1] and so my interest is always piqued when I see it come up for discussion — so then I see it mentioned in parliament by Jim Shannon in the context of privacy & safety: I will come to the horrific case raised by Theresa Villiers. On 12…
-
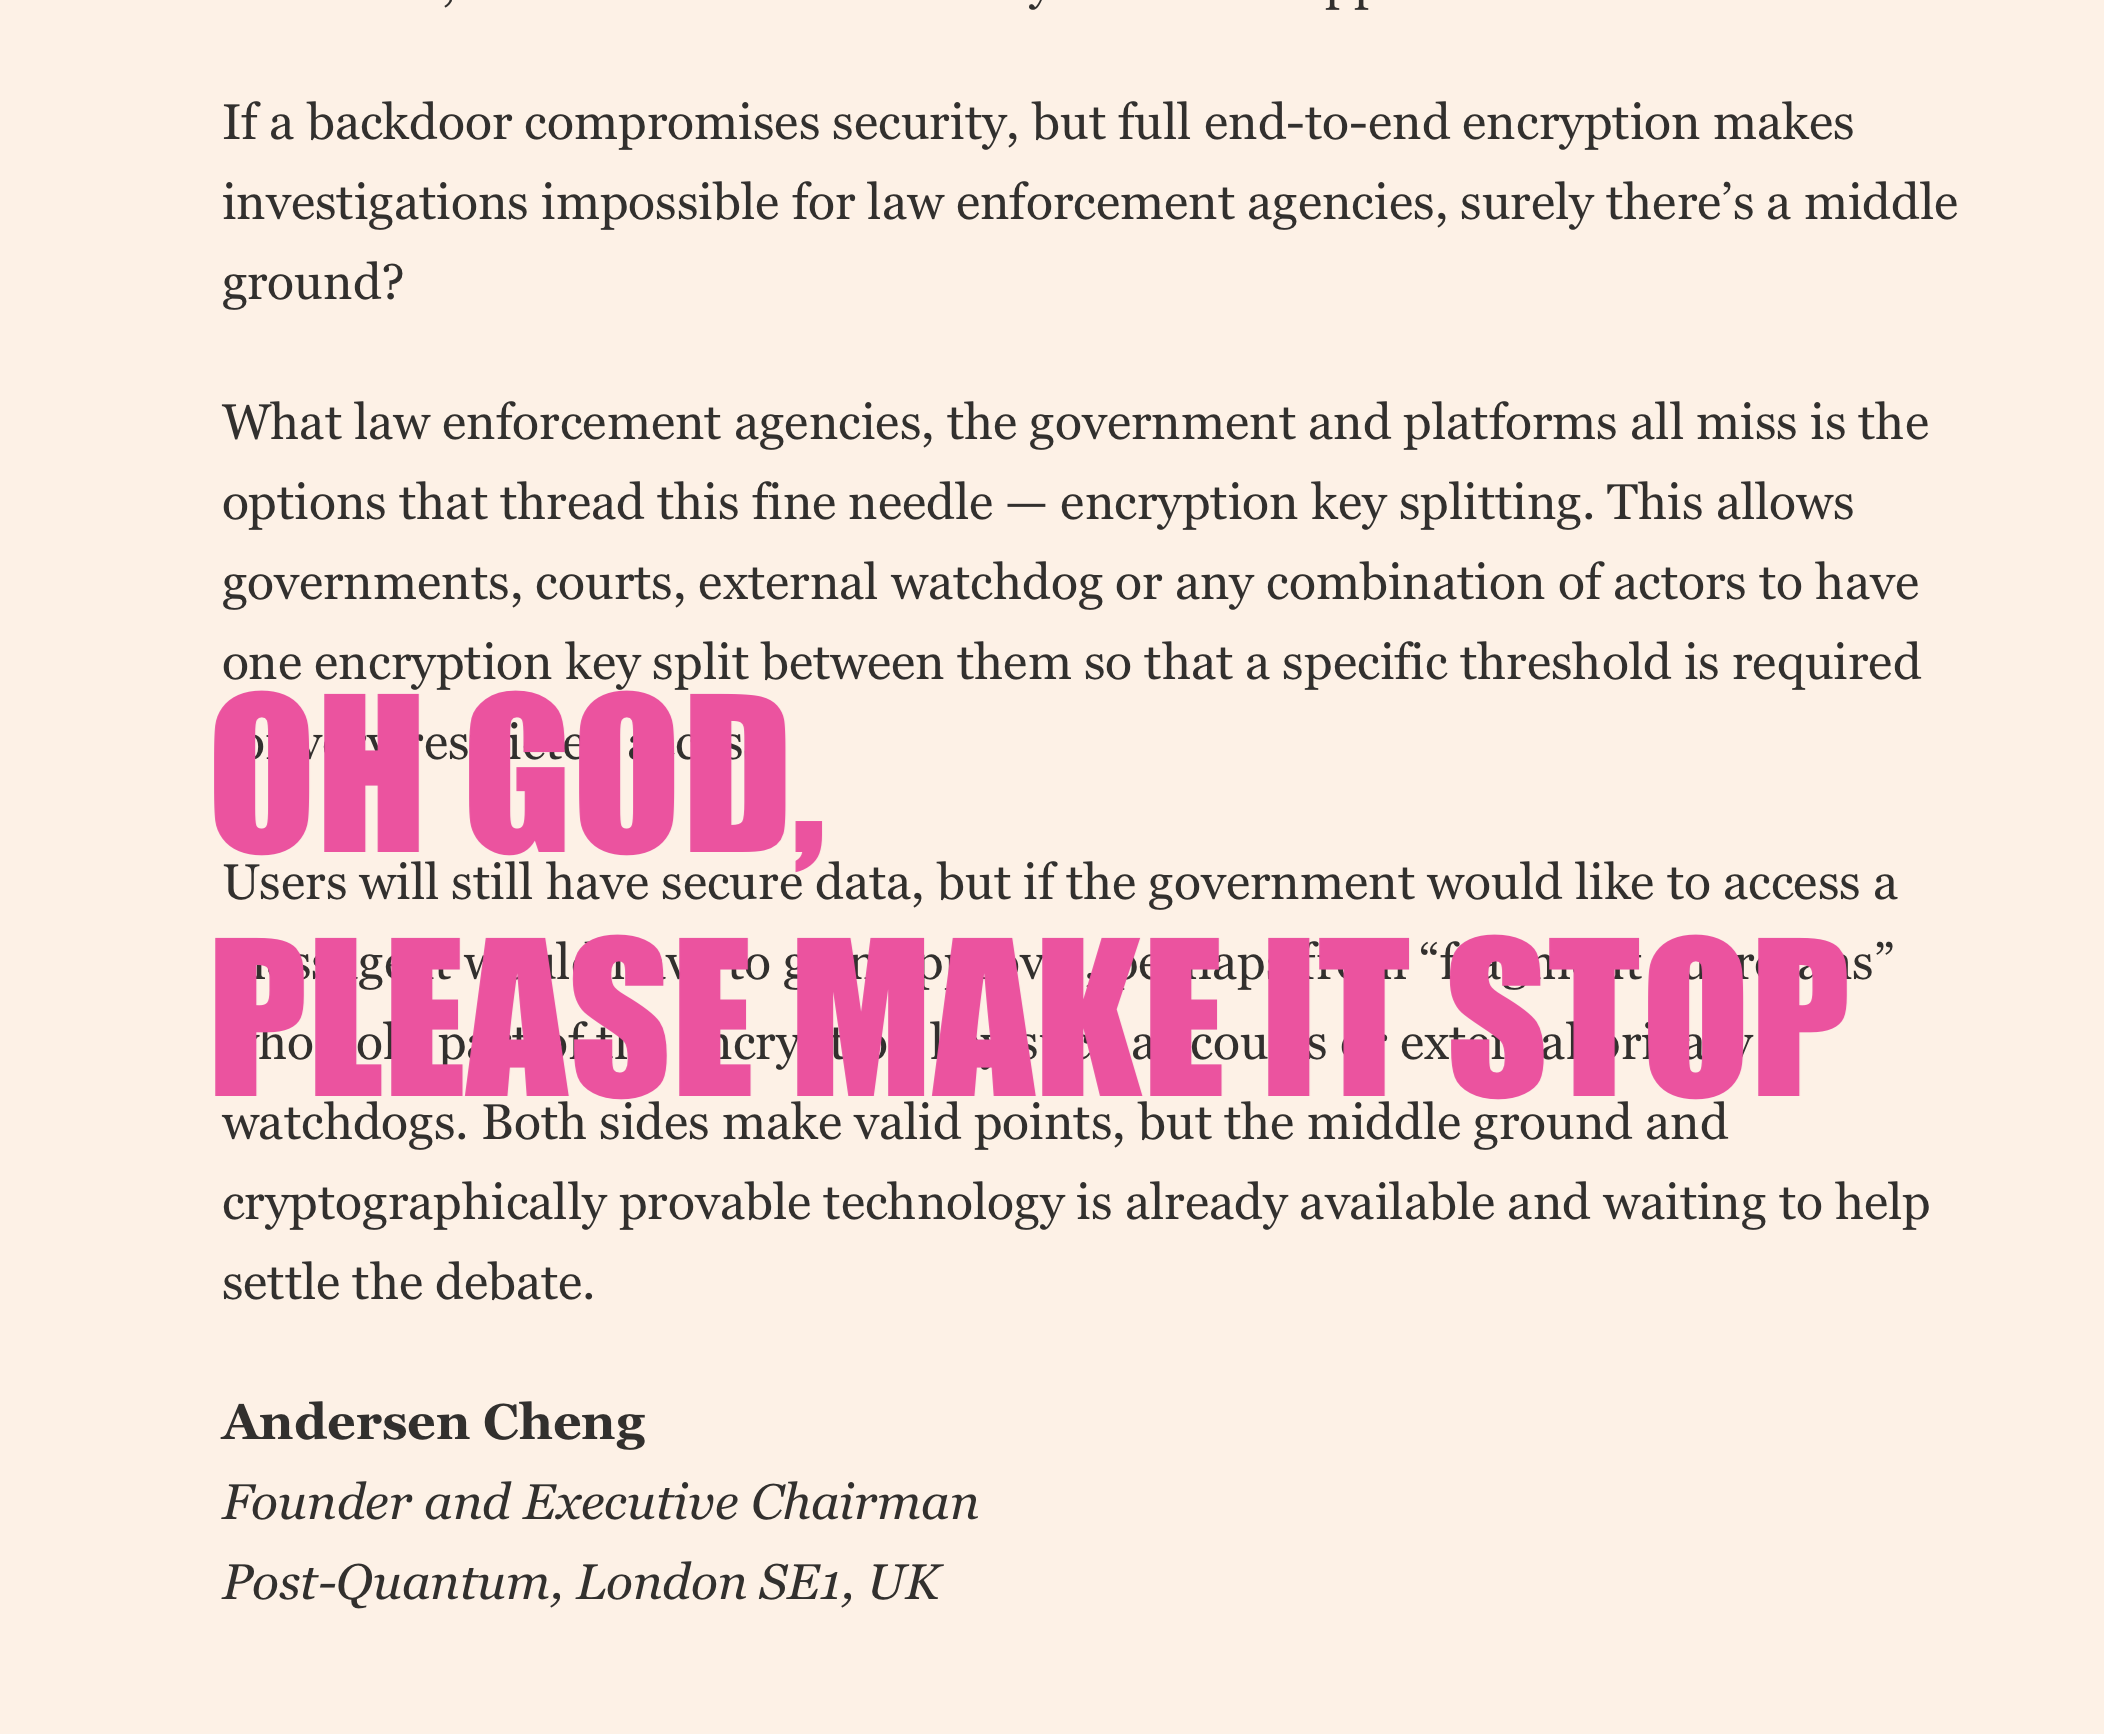
#Facepalm — what we really don’t need right now is somebody trying to reboot failed 1997 #Encryption Key Escrow, e.g. like in this letter to the @FT #OnlineSafetyBill
This is disappointing, misconceived, and woefully repetitious of some nonsense which we last (?) saw back in 1996/ish when secret-sharing was still relatively new, cool & trendy. In case you’re not familiar: this proposal (a) will not scale to meet demand nor growth (b) is in any case an illiberal imposition, (c) breaks Ranum’s Law…
-
Fixing: EXPKEYSIG 74A941BA219EC810 deb.torproject.org
Are you seeing this? W: An error occurred during the signature verification. The repository is not updated and the previous index files will be used. GPG error: https://deb.torproject.org/torproject.org bionic InRelease: The following signatures were invalid: EXPKEYSIG 74A941BA219EC810 deb.torproject.org archive signing key If so, do this: sudo apt-key adv \ –keyserver keyserver.ubuntu.com \ –recv-key 74A941BA219EC810 …which…
-
Response to “Most People Don’t Need End-to-End Encryption, Most of the Time” #NothingToHide #NothingToFear #DrinkableWater #OnlineSafetyBill
> Flip that around, secure encryption is an edge case compared to the majority, like your examples, that just want to message family. Yes that’s correct! But it’s also a *general good* as infrastructure, because [end to end encryption] de-risks all communication from hacking/exfiltration. It’s a bit like “make all water served through the domestic…
-
How WhatsApp could shut down service to the UK using “Feature Flags”
Speaking as a former Facebook engineer, I would expect pushing some kind of “feature flag” (global configuration option) which prevented the service connecting for people with a “+44” phone number. Pretty simple. Geo blocking could be done similarly. https://en.wikipedia.org/wiki/Feature_toggle?wprov=sfla1 2/n) When you’re coding for at-scale platforms you quickly realise the utility of creating a tool…
-

How the #OnlineSafetyBill’s OFCOM surveillance measures can (will?) bring about public emasculation of the UK Government and a kind of #CyberBrexit effect (HT: @ciaranmartinoxf @allanofhallam @wongmjane @jamesrbuk)
Background So I have been reading two recent think-pieces: Security services are in the market for as much information as they can get and if the threat of a decryption order may encourage a hesitant company to offer other useful data in order to avoid this being carried out then they will see this as…
